Networked and Exposed: The Security Reckoning Hiding Inside Your Connected Home
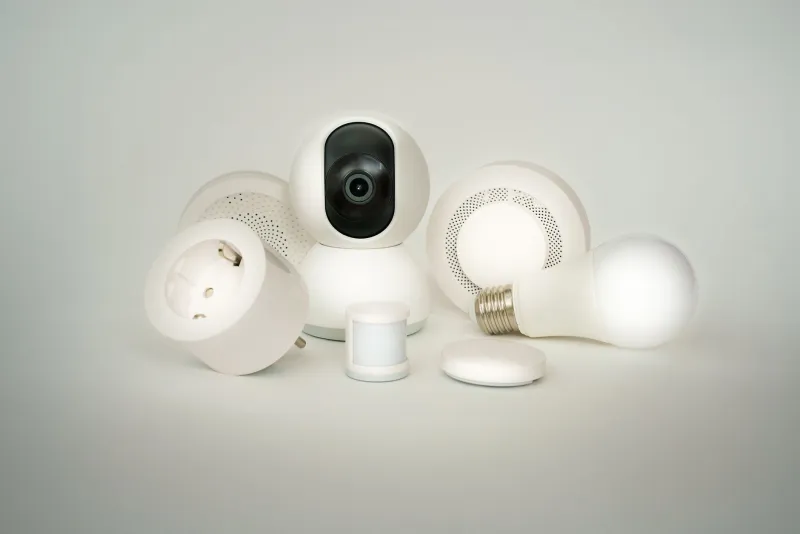
The pitch is always the same: seamless, effortless, intelligent living. Adjust your thermostat from the office. See who is at the door before you leave the couch. Track your sleep, your steps, your heart rate. The consumer Internet of Things market in the United States is projected to surpass $100 billion in the coming years, built on the promise that connectivity improves life. What the marketing materials rarely mention is what that connectivity costs in terms of security — and who ultimately pays when it goes wrong.
The answer, consistently, is the consumer.
A Market Built on Convenience, Not Security
The economics of IoT manufacturing create a structural bias toward features over protection. Devices compete on price and capability. Security hardening — the process of removing unnecessary services, enforcing strong default credentials, implementing encrypted communications, and committing to long-term firmware updates — adds cost and development time without adding visible value to a box on a retail shelf.
The consequences of this calculus are well documented. In 2016, the Mirai botnet recruited hundreds of thousands of IoT devices — cameras, routers, and digital video recorders — into a network used to launch some of the largest distributed denial-of-service attacks ever recorded, temporarily taking down major internet infrastructure including DNS provider Dyn. The devices were compromised not through sophisticated exploitation but because they shipped with default usernames and passwords that their owners never changed and that manufacturers never required them to change.
Nearly a decade later, the core problem persists. A 2023 report from security firm Bitdefender, which analyzed data from its consumer network protection product, found that IoT devices accounted for a disproportionate share of vulnerabilities detected on home networks, with smart televisions, IP cameras, and network-attached storage devices among the most frequently exploited categories.
What Attackers Actually Want From Your Smart Doorbell
The intuitive assumption is that attackers targeting home IoT devices are after the device itself — its video feed, its data, its functionality. Sometimes that is true. Documented cases include Ring and Nest camera hijackings in which attackers accessed live feeds and, in disturbing incidents, spoke to children through the device's speaker.
But the more consequential threat is lateral movement. A compromised IoT device sitting on the same network as a laptop, a smartphone, or a network-attached storage drive becomes a foothold from which an attacker can probe and potentially access far more sensitive systems. The smart thermostat that cannot be directly monetized may serve as the entry point to a home computer that can.
This is not a hypothetical scenario. Researchers at the American University's Cybersecurity program and independent security firms have repeatedly demonstrated in controlled environments that common consumer IoT devices — including popular models of smart plugs, baby monitors, and fitness hubs — can be compromised and used to scan adjacent network devices. The technique requires no advanced capability once initial access is obtained.
Cloud dependencies introduce an additional dimension of risk. Most IoT devices do not operate autonomously; they communicate with manufacturer cloud services to enable remote access and software updates. When those cloud services are breached — as occurred with the Verkada camera platform in 2021, exposing footage from 150,000 cameras including those in hospitals and jails — the exposure extends to every device connected to them, regardless of how securely the individual consumer had configured their own network.
The Update Problem
Firmware updates are the primary mechanism through which manufacturers can address newly discovered vulnerabilities. The IoT ecosystem's relationship with updates is, charitably described, inconsistent.
Many devices ship with no automatic update mechanism. Others receive updates for a defined support period — often two to three years — after which the manufacturer moves on and the device continues operating on vulnerable firmware indefinitely. Consumers, unaware that their three-year-old smart speaker is no longer receiving security patches, have no reason to replace a device that functions perfectly well for its intended purpose.
The National Institute of Standards and Technology has published IoT cybersecurity guidance, and the Biden administration's 2024 Cyber Trust Mark program — a voluntary labeling initiative designed to help consumers identify more secure IoT products at the point of purchase — represents a step toward market accountability. But voluntary programs depend on manufacturer participation and consumer awareness, both of which remain works in progress.
A Practical Framework for Managing IoT Risk
The goal for most consumers is not to eliminate smart devices — it is to contain the risk they introduce without sacrificing the utility that motivated the purchase. Several concrete measures significantly reduce exposure.
Segment your network. Most modern home routers, including those provided by major US internet service providers, support the creation of a guest network or a separate VLAN. Placing IoT devices on an isolated network segment prevents them from communicating directly with computers and smartphones on your primary network. A compromised smart refrigerator on a segmented network cannot reach your laptop. This is the single most impactful structural change a home user can make.
Change default credentials immediately. Every device that ships with a default username and password — and many still do — should have those credentials changed before the device is connected to your network. Use a unique, complex password for each device. A password manager can store these without requiring you to remember them.
Audit your device inventory. Make a list of every device connected to your home network. Most router management interfaces display connected devices; third-party apps such as Fing can provide a more detailed inventory. If a device is no longer in use, disconnect it. Dormant devices receiving no attention still present an active attack surface.
Check for and apply firmware updates manually. Do not assume that automatic updates are enabled or functioning. Log in to each device's management interface periodically and check for available updates. If a device has not received a firmware update in over a year and the manufacturer cannot confirm ongoing support, treat it as a security liability.
Research before you buy. Before purchasing a new connected device, spend five minutes investigating the manufacturer's security track record. Have they disclosed and patched vulnerabilities promptly? Do they commit to a specific support period in writing? Do they participate in the Cyber Trust Mark program? These questions are worth asking before the device is on your network.
Convenience Has a Price
The connected home is not going away. The devices are useful, the ecosystem is growing, and the convenience they deliver is real. What must also be real is the acknowledgment that each device added to a home network is a decision with security implications — implications that manufacturers have not consistently accounted for on the consumer's behalf.
Until regulatory frameworks mature and market incentives more reliably reward security investment, the responsibility for managing that risk sits with the individual. The steps above are not technically demanding. They are, however, necessary — and taking them is the difference between a smart home that works for you and one that quietly works against you.